Notice. New forum software under development. It's going to miss a few functions and look a bit ugly for a while, but I'm working on it full time now as the old forum was too unstable. Couple days, all good. If you notice any issues, please contact me.
ManiB Senior Member Joined: 12/10/2019 Location: GermanyPosts: 173
Posted: 08:03am 26 Sep 2026
Copy link to clipboard
Print this post
Hi Jim,
I wanted to update my MMEdit installation from V5.2.9 to the current version and downloaded MMEdit.zip from Geoff's official website.
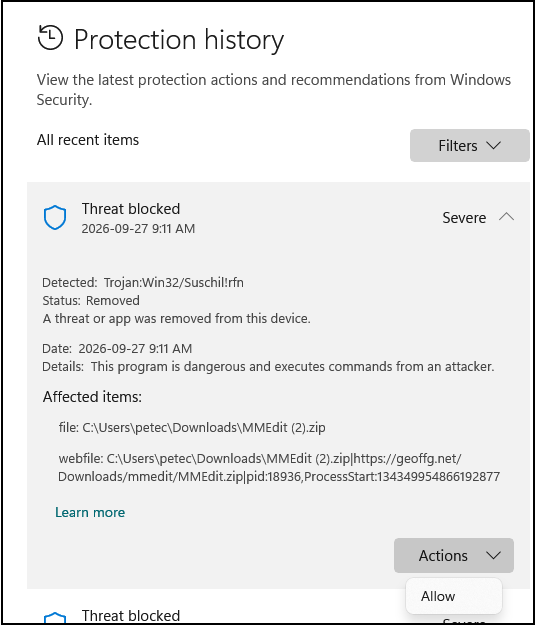
Windows Defender immediately removed the downloaded ZIP file and reported: Trojan:Win32/Suschil!rfn
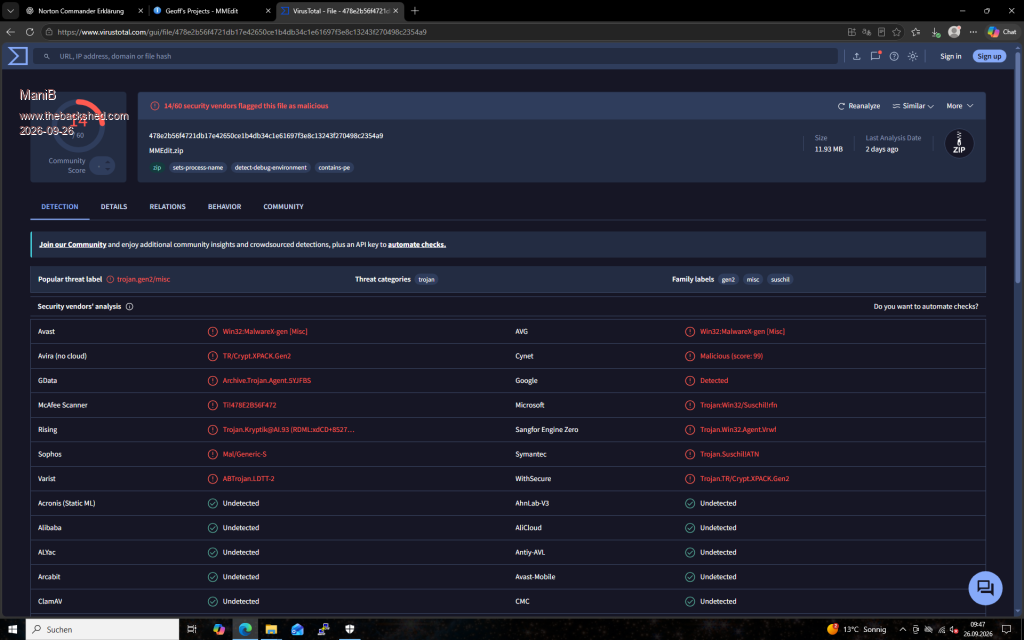
I therefore checked the file with VirusTotal. The result surprised me: 14 out of 60 security vendors currently flag MMEdit.zip as malicious.
The SHA-256 reported by VirusTotal is: 478e2b56f4721db17e42650ce1b4db34c1e61697f3e8c13243f270498c2354a9
The ZIP file is shown as 11.93 MB and was downloaded from: https://geoffg.net/Downloads/mmedit/MMEdit.zip
I have not overridden the Defender warning or executed anything from the ZIP so far. Is this a known false positive with the current MMEdit/MMCC version, or could there possibly be a problem with the current download package?
I'm happy to provide screenshots of the Defender and VirusTotal results if useful.
Regards, Manfred
TassyJim Guru Joined: 07/08/2011 Location: AustraliaPosts: 6619
Posted: 08:22am 26 Sep 2026
Copy link to clipboard
Print this post
I am sorry, I am not going to waste my life trying to get antivirus vendors to produce better products.
I have not knowingly included any nasties in MMEdit
ville56 Guru Joined: 08/06/2022 Location: AustriaPosts: 621
Posted: 08:53am 26 Sep 2026
Copy link to clipboard
Print this post
ManiB,
just test-downloaded it from Geoffs page ... no warnings at all from Defender here.
Gerald 73 de OE1HGA, Gerald
Peter63 Senior Member Joined: 28/07/2017 Location: SwedenPosts: 214
Posted: 01:31am 27 Sep 2026
Copy link to clipboard
Print this post
I don't have the latest version, so I tried downloading the MMEdit.zip file, from Geoff's page: https://geoffg.net/mmedit.html Windows 11 reports that it contains a virus.
I think that Windows 11, Smart App Control, is blocking this when I try to download it.
tested Smart App Control , to OFF, still blocking...??
I downloaded the MMBasic.zip file on my Raspberry Pi 5 computer. Transferred the file to a Windows 11 computer and ran a virus scan.
Trojan:Win32/Suschil!rfn
I had the MMEdit.zip file on a USB drive, and I chose for Windows 11 to take action on the file. Windows 11 deleted the file from my USB drive.
/Peter63 Edited 2026-09-27 12:04 by Peter63
TassyJim Guru Joined: 07/08/2011 Location: AustraliaPosts: 6619
Posted: 05:30am 27 Sep 2026
Copy link to clipboard
Print this post
I scan the contents of MMEdit.zip before updating. I occasionally download the zip from Geoff's site and sometimes Windows Defender has a bitch. Today, the downloaded zip was quarantined. I un-quarantined it and extracted to a folder. I then asked Defender to scan the folder. "No virus found"
In other words, Today, Windows Defender is not happy with the ZIP but is happy with the contents.
Tomorrow I can do the same thing and get different results.
Last time I tried to submit the zip to VirusTotal it refused to accept the zip. I have given up trying. When it was accepting the zip, the best I could manage is 2 or 3 malicious flags.
Back when I had time to waste, I used to try and get more information from the AV vendors. Just saying there is a virus type xxx is not much use when there are 700 files in the zip. The best reply I ever managed was from Norton; "We will get back to you within 2 weeks" Still waiting 5 years later.
It is good to be careful but there is nothing I can do about it. I don't think I can tell Claude to tell his mates to leave me alone
PeteCotton Guru Joined: 13/08/2020 Location: CanadaPosts: 657
Posted: 03:27pm 27 Sep 2026
Copy link to clipboard
Print this post
For the sake of science I tried it as well and got the same "virus detected" result (Windows 11).
I opened Windows Security (Just click the windows menu button and type in "Windows Security") and then click on "Protection History". It shows the blocked file.
Click on the blocked file and under "Actions" click "Allow".
Now you can go back to the website and download it without issue.
I think this is important, because in my view, MMEdit is an absolutely critical part of the Maximite Development chain. Not being able to download it would be a tragedy for the mite community.
ManiB Senior Member Joined: 12/10/2019 Location: GermanyPosts: 173
Posted: 08:22pm 27 Sep 2026
Copy link to clipboard
Print this post
Thanks Jim, Peter and Pete for testing this.
For the sake of science, I did a few more tests. :-)
I downloaded the original MMEdit.zip again. The SHA-256 is still:
So it is exactly the same file I originally tested.
I then extracted the ZIP and scanned the complete extracted folder with Windows Defender. Just as Jim reported, Defender found no threats.
I also repacked the unchanged files into a new ZIP. Defender was happy with that ZIP as well, although VirusTotal still reported 12/67 detections.
The most interesting result came from testing some of the files separately with VirusTotal:
MMedit5_32_64.exe (installer): 14/71 detections
MMEdit5_XP_portable.zip: 1/55 detections
MMEdit.exe: 1/71 detections
So the majority of the detections seem to be associated with the MMedit5_32_64.exe installer rather than MMEdit.exe itself.
For now I will simply use the portable version and avoid the installer. That works fine for me and I think I've done enough antivirus testing for one weekend. :-)
Thanks again everyone for checking and comparing the results.
Manfred
PS: I have now started MMEdit V5.4.3 from the portable package successfully. Windows SmartScreen displayed the expected "unknown publisher" warning because MMEdit.exe is unsigned, and Windows Firewall asked for network access, but Defender did not report any malware. Edited 2026-09-28 06:31 by ManiB
TassyJim Guru Joined: 07/08/2011 Location: AustraliaPosts: 6619
Posted: 08:41pm 27 Sep 2026
Copy link to clipboard
Print this post
The installer contains 2 different versions of MMEdit.exe 32bit and 64 bit. The ZIP contains a different version 32 bit but compiled using an earlier compiler to allow XP.
That's 3 versions of MMEdit.exe (not counting the 2 Linux versions). Each version is likely to give different results.
Same as MMCC.exe
I don't know how much longer the portable version will support XP. When that happens, the portable MMEdit.exe will be the same as the 32bit one in the installer.
When I stop making changes, the problem will diminish and eventually go away. That is one solution.
ManiB Senior Member Joined: 12/10/2019 Location: GermanyPosts: 173
Posted: 09:20pm 27 Sep 2026
Copy link to clipboard
Print this post
Thanks Jim, that explains the different VirusTotal results. I'll stick with the portable version for now. It runs fine on my system and Defender is happy with it. Manfred
JohnS Guru Joined: 18/11/2011 Location: United KingdomPosts: 4385
Posted: 09:56pm 27 Sep 2026
Copy link to clipboard
Print this post
Some antivirus programs use quite crude tests to try to detect bad stuff, so get it wrong when a file happens to trigger them.
I'd rather trust Jim :)
John
Grogster Admin Group Joined: 31/12/2012 Location: New ZealandPosts: 10049
Posted: 10:46pm 27 Sep 2026
Copy link to clipboard
Print this post
.....and yet again.....W11 is the source of much unnecessary pain.
At this point, I almost consider W11 itself to be something of a malware more then an OS. Crap like this, bloody ad pop-ups, f-ing co-pilot forced into every corner of the OS and anything that runs on it, constantly offering suggestions you never asked for, slow PC performance.....the list goes on.
Many of the AV softwares are known for generating false-positives, ESPECIALLY the trial versions, as they OFTEN give false positive results(by design), in an attempt to get you to purchase a subscription to their software. If you do that, the next scan miraculously shows ZERO problems - but that was cos of a virus database update, naturally, not cos you just bought a subscription....
AV softwares like to use scare-tactics to try to get the user to panic and fork over cash for subscriptions to AV software they could probably easily do without.
MOST of the nasties now, are in the form of email scams and phishing, more then viruses hiding in the background. Not to say that viruses aren't still an issue - they are - but most scams now pretend to be some other website via emails or malware pop-ups.
Here in New Zealand, every few years, a common email scam resurfaces and pretends to be from either the New Zealand Police, or Inland Revenue - and threatens penalties from mega-buck fines to arrest for NOT paying an outstanding fine....a fine that does not exist, cos you were never fined for anything - it is a lie.
But the scams LOOK authentic, as the scammers have copied the entire genuine website, all the graphics and everything, and just change any links to pages that attempt to steal your CC details. Older folk are easily scammed this way, cos they just BELIEVE that the emails are genuine, cos they have all the authentic Police or IRD logos and graphics. Sometimes a phone number is given, but that just lets you call up the scammer, rather then the scammer calling you for a change.Smoke makes things work. When the smoke gets out, it stops!

 Notice. New forum software under development. It's going to miss a few functions and look a bit ugly for a while, but I'm working on it full time now as the old forum was too unstable. Couple days, all good. If you notice any issues, please contact me.


 Print this post